Delivered · In daily use
RiskTech Control
DifferentHide product (same client) · AWS ops & governance console · 8+ modules
1 console replaced 4+ AWS tools
Introduction
RiskTech Control is DifferentHide's internal operations and governance console for platform engineers managing AWS infrastructure, compliance, and cost. Working with the UK platform team, I designed the product IA, built the web frontend across eight modules, and shipped it for daily use while backend integration continues.
Challenge
Platform teams juggled separate tools for EC2 state, EKS workloads, endpoint checks, S3 log hunts, and cost spreadsheets. Compliance evidence lived in exports nobody wanted to rebuild before audits. The UI had to be dense, permission-aware, and safe for production operations, and it had to exist in code, not slide decks.
Research
- Shadowed how platform engineers hopped across AWS consoles for EC2, EKS, endpoints, logs, and cost views before a single ops day was done.
- Mapped ISO supplier evidence gaps with the platform team: what auditors asked for versus what lived in one-off exports and spreadsheets.
- Checked dense enterprise UI carefully for permission risk. Wrong access on a production action is worse than a missing shortcut.
Approach
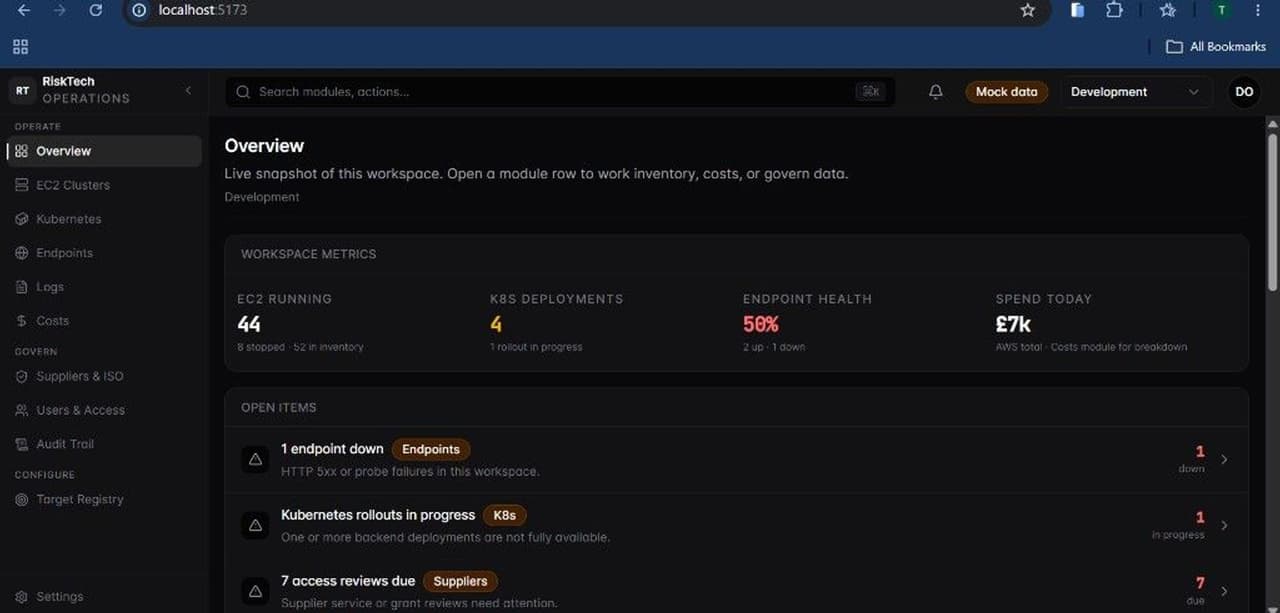
- Organised the product into three planes (Operate, Govern, Configure) so daily ops, compliance, and chargeback setup stay separate but connected.
- Designed a permission-aware overview: KPI strip plus module tiles that hide when the user lacks access.
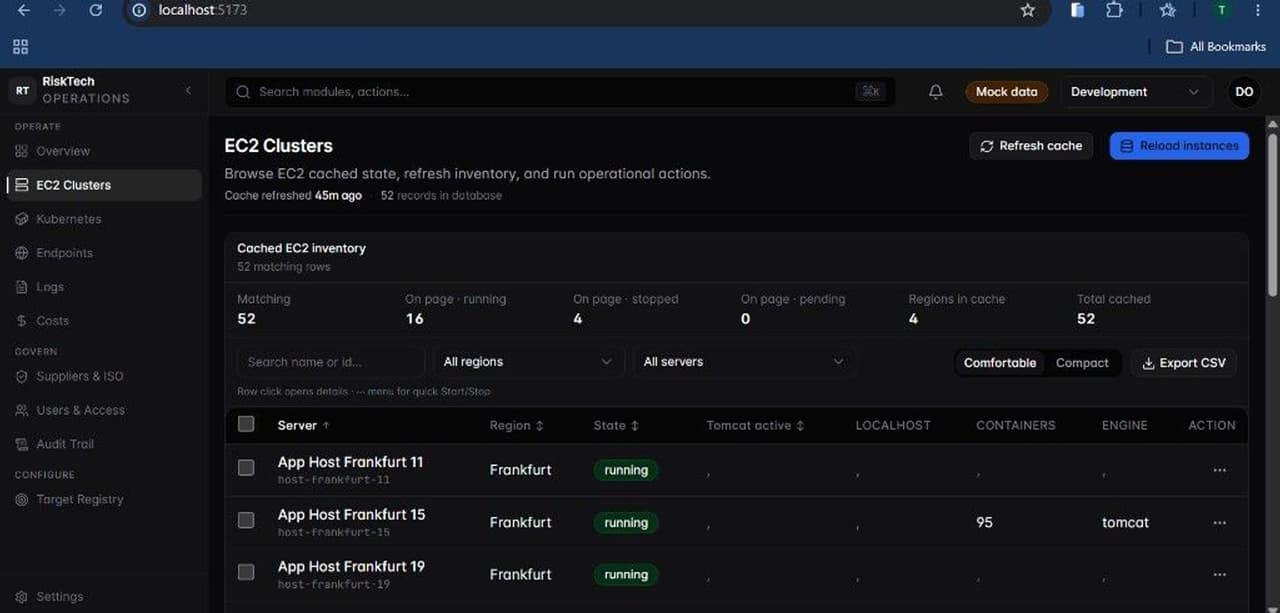
- Built safe operational flows for EC2 and Kubernetes with confirmation on destructive actions, production safety banners, and immutable audit logging.
- Developed the web frontend across modules with mock APIs while backend integration rolled out module by module alongside engineering.
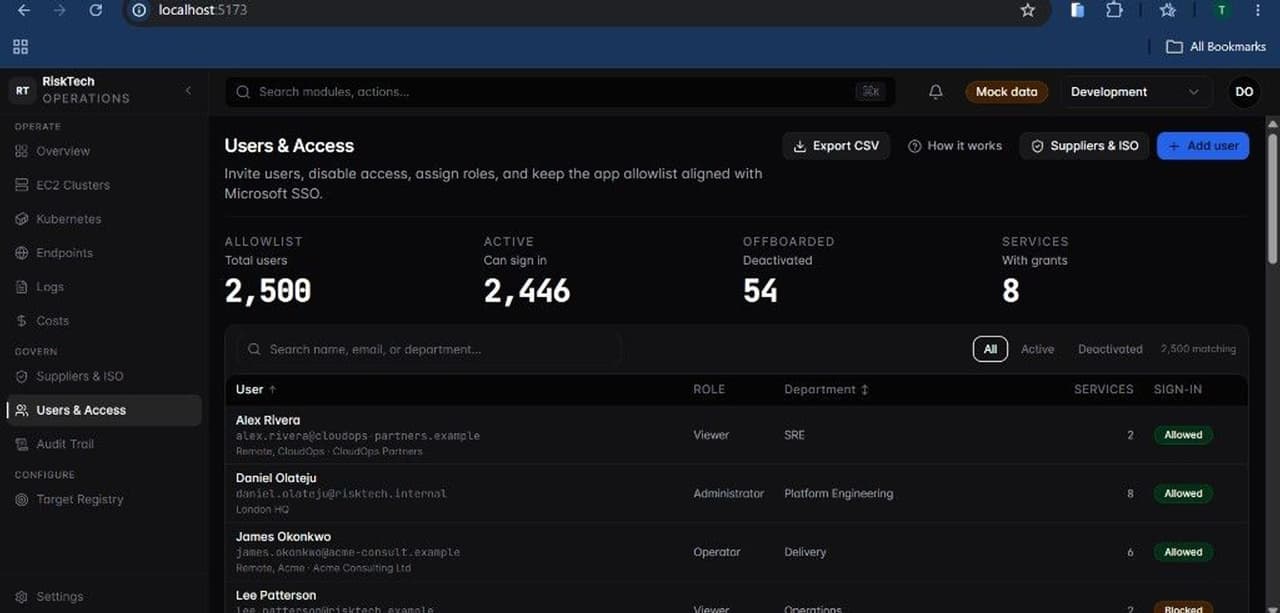
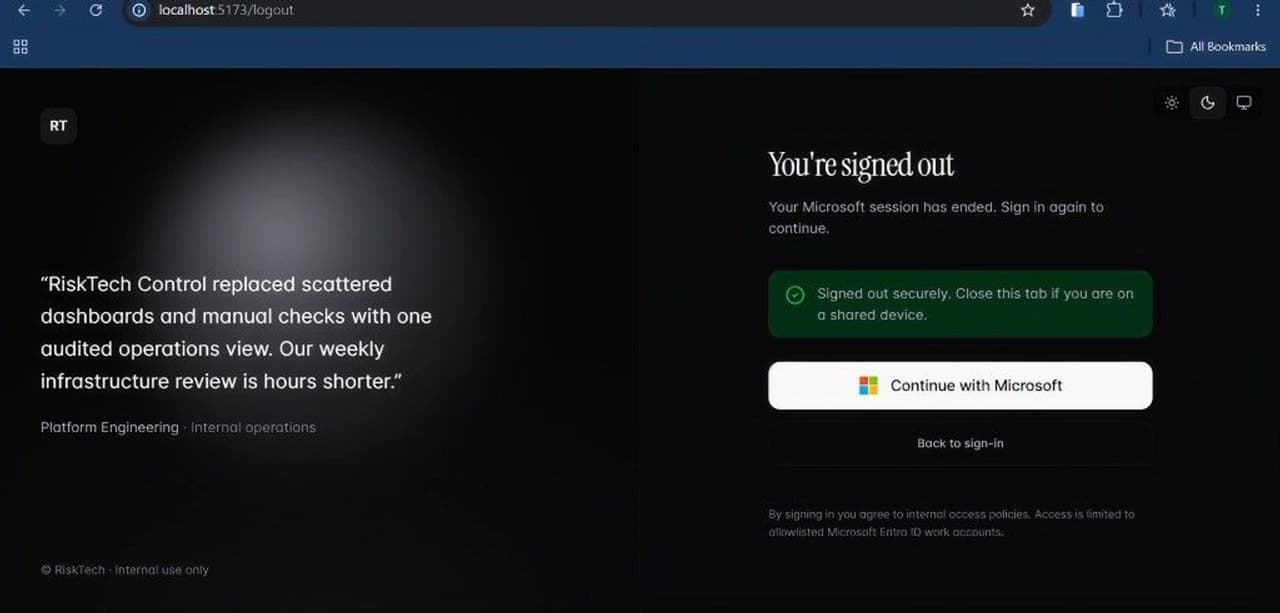
- Shipped a dense enterprise shell: Microsoft SSO allowlist, environment switcher, command palette, and light/dark themes for long review sessions.
- Mapped ISO supplier evidence and cost views so audit prep did not depend on manual spreadsheet rebuilds.
Decisions
- Split the product into Operate, Govern, and Configure planes so daily infra work never competed with audit prep in the same mental model.
- Tried greying out modules the user could not access. Operators still clicked them and hit dead ends, so we hid unavailable modules instead, permission boundaries stayed obvious under pressure.
- Required confirmation, production banners, and immutable audit logging on destructive EC2 and Kubernetes actions before shipping the ops flows.
Impact
- 8+ modules shipped: EC2, Kubernetes, endpoints, costs, suppliers/ISO, audit trail, and more.
- DifferentHide platform team uses the console daily for infrastructure and ISO workflows.
- Replaced console-hopping across 4+ separate AWS tools with one permission-aware UI.
- ISO supplier evidence exports cut manual spreadsheet work before audit reviews.
Hiring or building something similar?
Send a short note with the product, timeline, and what you need. I read these myself and usually reply within one business day.